For more than two decades, formal cybersecurity risk assessments were mainly a concern for healthcare organizations and financial institutions. HIPAA has required them since 2003, and the New York Department of Financial Services (NYDFS) has built its Part 500 cybersecurity regulation around them since 2017. New California Consumer Privacy Act (CCPA) regulations, in effect since January 1, 2026, now extend similar expectations to businesses in nearly every industry.
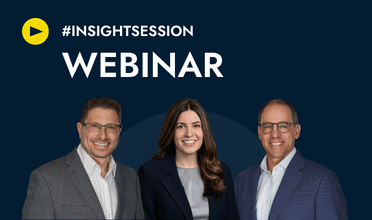
These requirements raise the stakes for every assessment an organization performs. Businesses must certify to regulators that their audit is complete, and regulators can request the underlying audit report, so it makes sense to prepare every assessment as if it could be reviewed.This topic was a central theme of Myna Partners recent webinar, Before the Breach: What a Cybersecurity Assessment Reveals About Your Security Program.
What do the new CCPA cybersecurity audit rules require?
The CCPA regulations require two things: an annual cybersecurity audit under Article 9 and risk assessments for high-risk processing under Article 10.
Article 9 covers annual cybersecurity audits. An independent auditor must assess whether the business’s security program is adequate to protect personal information. The requirement applies to businesses that meet either of these thresholds:
- Deriving 50% or more of annual revenue from selling or sharing personal information
- Having annual gross revenues above $25 million (adjusted for inflation, currently $26,625,000) and, in the preceding calendar year, processing the personal information of 250,000 or more consumers or households, or the sensitive personal information of 50,000 or more consumers
The regulations also set the scope of the audit. They list 18 assessment topics that must be tested where they apply to the business:
- Authentication
- Encryption
- Account management and access controls
- Inventory and management of personal information and systems
- Secure configuration of hardware and software
- Internal and external vulnerability scans, penetration testing, and vulnerability disclosure and reporting
- Audit-log management
- Network monitoring and defences
- Antivirus and antimalware protections
- Segmentation of an information system
- Limitation and control of ports, services, and protocols
- Cybersecurity awareness
- Cybersecurity education and training
- Secure development and coding best practices
- Oversight of service providers, contractors, and third parties
- Retention schedules and proper disposal of personal information
- Incident response management
- Business continuity and disaster recovery plans
Article 10 covers risk assessments. Businesses must also assess specific processing activities that present a significant privacy risk. These work much like privacy impact assessments, weighing whether a particular use of personal or sensitive personal information should happen at all given its potential harm to consumers. A qualified member of executive management with direct responsibility for compliance can lead them.
The audit requirements phase in by annual revenue:
| Annual revenue | Audit period | First certification due |
| More than $100 million | January 1, 2027 to January 1, 2028 | April 1, 2028 |
| $50 million to $100 million | January 1, 2028 to January 1, 2029 | April 1, 2029 |
| Less than $50 million | January 1, 2029 to January 1, 2030 | April 1, 2030 |
Risk assessment submissions under Article 10 are first due April 1, 2028.
For both requirements, the business must certify to California’s privacy regulator that the work is complete. Companies don’t have to file the underlying reports, but the regulator can request them at any time, and they must be produced within 30 calendar days. Because an executive signs the certification, a weak or inaccurate assessment creates both personal and organizational exposure.
Falling short also has a measurable price. IBM’s Cost of a Data Breach Report 2026, conducted by Ponemon Institute, found that noncompliance with regulations added an average of $201,112 to the cost of a breach.
How will regulators use your cybersecurity assessment?
Regulators are likely to treat your assessment as evidence. After an incident, they can review it to see which gaps you knew about and whether you fixed them.
New York offers a useful preview. Under NYDFS Part 500, the risk assessment is the foundation of a company’s cybersecurity program, which makes past assessments among the first documents reviewed after an incident. They show when the program changed and which findings were left open. California’s certification and production requirements suggest CCPA assessments could be used the same way.
Regulators are also only one possible audience. If an incident leads to a class action or other litigation, the same reports may be discoverable by opposing counsel.
How can you run a cybersecurity assessment without creating legal liability?
Organizations can get the full value of an assessment while managing how its findings are documented. These five practices help:
- Consider a readiness assessment through counsel. Any readiness assessment helps you find and fix problems before the independent auditor arrives. Conducting it through legal counsel, potentially under attorney-client privilege, can also keep the issues you identify and remediate confidential. The same approach is useful ahead of ISO 27001 certification or a SOC 2 audit.
- Read the report the way an adversary would. Before the report is final, legal and compliance reviewers should look for language someone could later pull out to explain why an incident happened.
- Only commit to deadlines you can keep. The CCPA audit report must include a management action plan and target date for every gap. A missed deadline on a critical finding that later contributes to an incident is the kind of record regulators look for. If a date has to slip, document the compensating controls and the reason.
- Build a process you can repeat. The regulations define what the audit must cover, and it happens every year. Assign clear owners for gathering evidence and budget for the same level of effort annually.
- Help IT give complete answers. Technical teams often answer assessment questions with a literal yes or no. Privacy and legal teams should help them explain the compensating controls, vendors, or workarounds behind a “no” so the assessor has the full picture.
When should you start preparing for a CCPA cybersecurity audit?
Organizations in the first tier should start now. Their first audit period opens January 1, 2027, and a typical assessment takes eight to twelve weeks. The audit also tests whether controls operate effectively across the entire audit period, so auditors draw samples from throughout the year. For first-tier companies, January 1, 2027 is the day clean evidence needs to begin. Myna recommends a readiness assessment before then, so there is time to remediate gaps before the audit period opens.
The regulations also reference NIST CSF 2.0 as a framework that can support the audit. Organizations that have already completed a NIST CSF assessment have a head start. They will still need to add effectiveness testing across the audit period and the CCPA’s required report contents: a description of the systems in scope, every policy and document evaluated, the effectiveness of each control, every gap identified, and a management action plan for each one.
Watch the full webinar
Before the Breach: What a Cybersecurity Assessment Reveals About Your Security Program is available on demand. Dave Cohen and Corey Gant of Myna Partners and Hannah Levin of Morgan, Lewis & Bockius LLP cover the regulatory landscape and walk through Myna’s assessment methodology. Watch the recording.
If your organization falls into the first CCPA audit tier, Myna Partners can help you scope and complete a readiness assessment. Contact our team to learn more.
Frequently asked questions about CCPA cybersecurity audits
Who needs a CCPA cybersecurity audit?
Businesses subject to the CCPA need an annual audit if they derive 50% or more of revenue from selling or sharing personal information, or if they exceed the CCPA revenue threshold and process the personal information of 250,000 or more consumers or the sensitive personal information of 50,000 or more consumers. Requirements phase in by revenue, starting with an audit period that opens January 1, 2027 for businesses with more than $100 million in revenue.
When is the first CCPA cybersecurity audit due?
For businesses with more than $100 million in revenue, the first certification is due April 1, 2028, covering the period from January 1, 2027 to January 1, 2028. Smaller businesses follow in 2029 and 2030.
Does a CCPA cybersecurity audit have to be independent?
Yes. An independent auditor must perform the Article 9 cybersecurity audit. Article 10 risk assessments can be led internally by a qualified member of executive management.
Do you have to submit the audit report to California regulators?
No, but the business must certify that the audit is complete. The regulator can request the underlying report at any time, and it must be produced within 30 calendar days.
Can NIST CSF be used for a CCPA cybersecurity audit?
Yes. The regulations reference NIST CSF 2.0 as a framework that can support the audit. An existing NIST assessment will still need effectiveness testing across the audit period and the CCPA’s required report contents.
Can a cybersecurity assessment be protected by attorney client privilege?
A readiness or gap assessment conducted through counsel can often be structured under attorney client privilege. Organizations should work with their legal counsel to set up the engagement correctly.
Related reading: Why Cybersecurity Gaps Stay Hidden Until a Breach, and How a Cybersecurity Assessment Finds Them First